Ask in plain language. Get answers from every business app you run — permission-checked, right inside Slack.
No control panel. The agent grants, revokes, and adjusts access in the conversation itself.
The deal is in HubSpot. The ticket is in Jira. The doc is in Confluence. The email is in Gmail. Your team plays detective instead of doing their job.
Most AI tools give everyone access to everything. That's not a feature — it's a liability. Sales shouldn't see HR data. Interns shouldn't see financials.
Generic AI doesn't know your processes, your org structure, or your data. It can't remember last week's conversation. It's a toy, not a tool.
A real conversation. Multiple tools queried. Access-controlled response. Seconds.
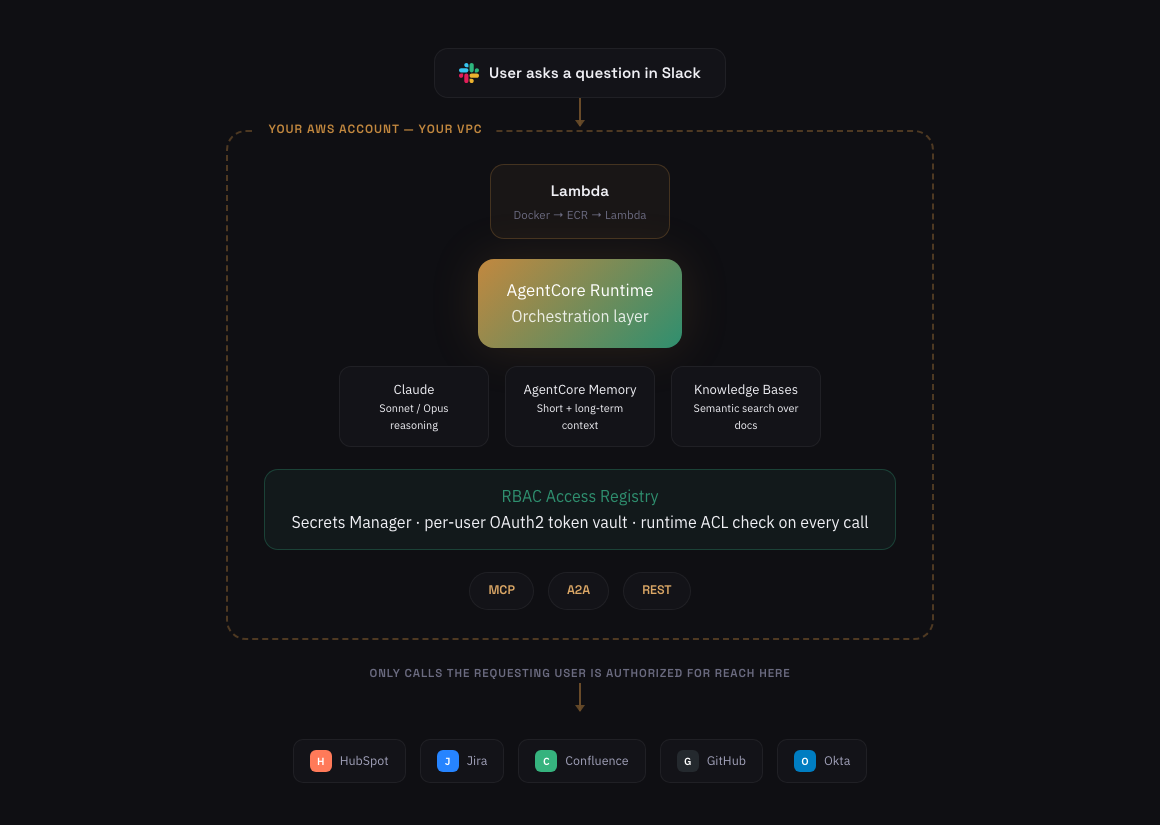
Deployed to your AWS account. Not ours — yours. Built on Bedrock AgentCore, powered by Claude. Your data never leaves.
MCP. A2A. REST. Whichever protocol fits — we're not locked to one. Every user authenticates individually. No shared accounts. Sales sees CRM. Engineering sees Jira. HR sees HR.
Natural language. No commands. No training. It cross-references tools, takes action, remembers context. Answers formatted the way Slack always has — read once, act. No follow-up questions.
Every app switch costs 23 minutes of refocus (UC Irvine research) — paid hours spent hunting for information, not closing deals or making decisions. That time goes back to the work that actually earns you money.
Runs on your AWS account, not ours. No one can hold your data hostage for a price hike later — because no one but you ever has it.
Set daily and monthly limits per person. See exactly who's using what. No surprise invoice at the end of the month — the ceiling is yours to set, not ours.
Deployed to your infrastructure the same day. Integrations connected in days. You're not funding a 6-month consulting clock — you're paying for a working product, immediately.
No shared bot account. Sales sees CRM. Finance sees financials. Someone leaves? Revoke access in seconds — nobody sees what they shouldn't.
40% of enterprise apps will run AI agents by year-end (Gartner) — yours can be one of the ones that actually ships. Live on your tools within a week. No multi-quarter evaluation, no science project.
MCP, A2A (Agent2Agent), or a direct REST call — we use whichever gets your system connected without re-architecting anything. Swap or add integrations without touching agent logic. No vendor lock-in.
Claude Sonnet/Opus backbone. AgentCore Runtime for orchestration. AgentCore Memory for short + long-term context. Bedrock Knowledge Bases for semantic search over your docs.
AccessRegistry in Secrets Manager. HMAC-verified, budget-gated before the model sees anything. The model never holds a credential — a trusted runtime mints per-user OAuth via AgentCore Identity and executes every call itself.
When the agent writes code to crunch your data, it executes in an isolated sandbox with a logs-only role — no S3, no DynamoDB, no Bedrock, no AWS access at all. Even fully attacker-controlled code has near-zero blast radius.
Data requests and deletions — automatic, full audit trail. Immutable logs, defined data flows, human oversight. One governance system satisfies them all.
Your AWS. Your VPC. Your encryption keys. We deploy, hand over the keys, and step back. We're consultants, not landlords.
New tool in your stack? We plug it in. No rebuilding, no downtime. If your tool has an API, it works.
Salesforce, Notion, Linear, Asana, Google Drive, SharePoint, Gmail, Outlook, Google Workspace, Azure AD, GitLab, ServiceNow — plus internal tools, legacy systems, and anything else with an API. We build the bridge.
We deploy a custom AI agent directly into Slack — the tool your team already lives in. It connects to all your business tools — CRM, project management, documentation, email, code repos, and more. Your team asks questions in natural language, and the agent finds answers across every connected tool in one response. Unlike generic AI assistants, it respects your org's access controls, remembers context across conversations, and runs on your own infrastructure.
Built-in AI assistants (Slack AI, Teams Copilot) only search within their own ecosystem — they can't query your CRM or project tools. Microsoft Copilot is locked to Microsoft products. ChatGPT Enterprise doesn't connect to your internal tools or enforce granular RBAC.
Cleavis is built for Slack specifically — deep native integration, not a generic bot ported over. It connects to any tool via MCP, A2A (Agent2Agent), or a direct REST API — whichever protocol the target system actually supports — enforces per-user access control at the tool and data level, provides both short and long-term memory, and runs entirely on your infrastructure. You own everything.
Here's the thing most people miss: the AI agent doesn't have a master key to your data. Each person logs in as themselves — their own credentials, their own permissions. The agent can only see what that person is already allowed to see in each tool.
So when a sales rep asks a question, the agent queries HubSpot as that sales rep — not as some all-seeing admin account. Ask about payroll? The agent doesn't "deny access." It simply has no way to get there. The door doesn't exist for that user.
On top of that:
No tool changes needed. The agent connects to your existing tools via API — nothing to replace, nothing to migrate.
Day 1: Agent template deployed to your AWS. Day 2-3: Integrations connected. Day 3-5: Access control configured, pilot users testing. Week 2: Full rollout with 15-minute training.
Yes. We connect via whichever protocol fits — MCP (Model Context Protocol), A2A (Agent2Agent), or a direct REST integration. We're not locked into one standard, so any tool with an API can be connected. We build custom integrations for internal tools, legacy systems, and proprietary databases as part of the engagement.
Tell us about your team and your biggest pain point. We'll reply with a tailored walkthrough — no sales pitch, no pressure, just a clear picture of how Cleavis fits your setup.
Reach us directly: talk@cleavis.eu